Secret management
Haven
BetaIt holds other systems’ credentials, so it fails closed.
A secret manager written in async Python on PostgreSQL. It is multi-tenant by row-level security, and a tenant is resolved from the credential presented and from nothing else, so no header and no parameter can select one. The master key exists only in memory and is reconstructed from three of five Shamir shares, which means a restarted Haven answers every route with 503 until an operator unseals it.
Who it is for. Teams holding credentials for other systems that want them issued with an expiry, scoped by policy, and recorded in an audit trail that can be checked.
- Status
- Beta
- Product site
- haven.rodmena.co.uk
- Tags
- Secret managementPostgreSQLShamir unsealLeasesTransitPKI
What it does
-
Sealed until an operator unseals it
The master key lives in memory and is reassembled from three of five shares. After a restart every route answers 503 until someone with a share acts.
-
The tenant comes from the credential
Each tenant has its own encryption key, mounts, policies and secrets, isolated in PostgreSQL by row-level security. A namespace header may only agree with the token it arrived with.
-
Credentials that expire
A database credential is minted per process and carries a lease. It is created in the target database and dropped when the lease is revoked or runs out.
-
Encryption as a service
Transit keys never leave Haven, so an application holds none. Every ciphertext names the key version that made it, and rotating a key leaves old ciphertext readable.
-
A private certificate authority
Short-lived certificates are issued per service, with the domains a role may ask for constrained by that role.
-
An audit trail that is checked
Every request is recorded before it runs, and each record is chained to the one before it by a hash. Verification walks the chain and recomputes it.
Documentation and access details are on the product site, haven.rodmena.co.uk. For a pilot, an integration or procurement questions, contact us.
Screens
All 6 screens of Haven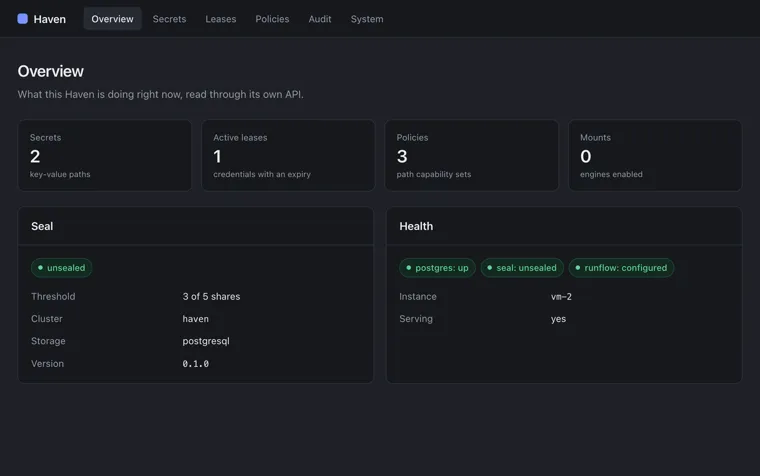
Overview Haven screenshot 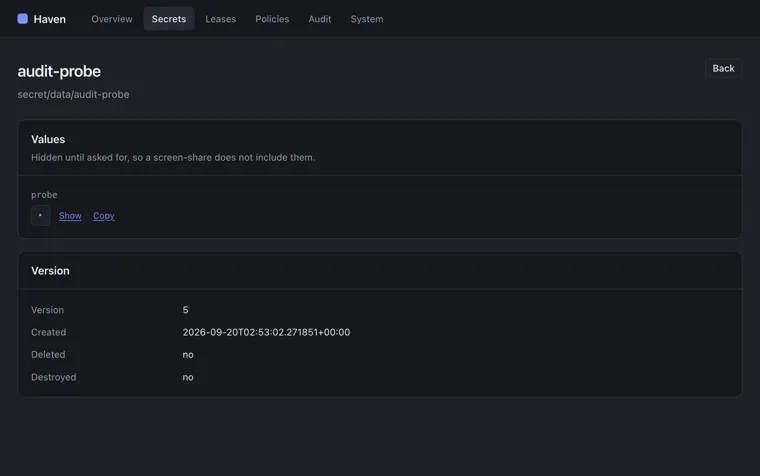
A stored secret Haven screenshot 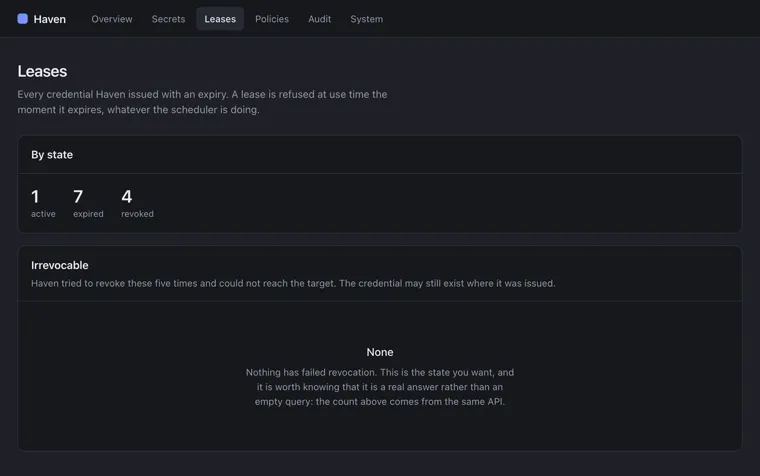
Leases Haven screenshot 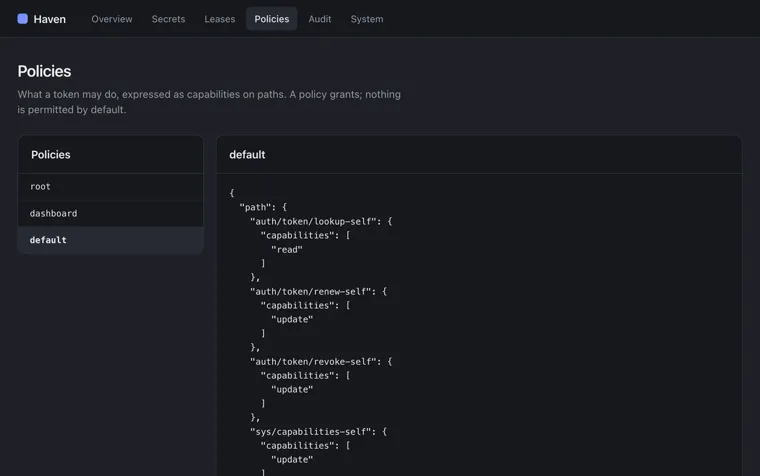
Policies Haven screenshot 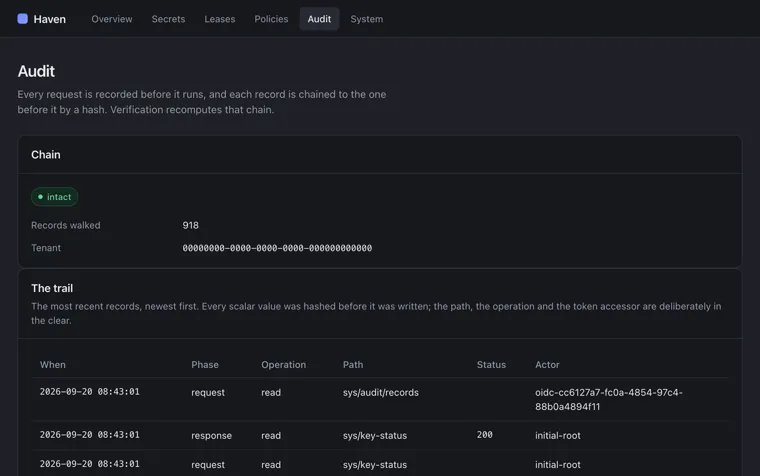
The audit trail Haven screenshot 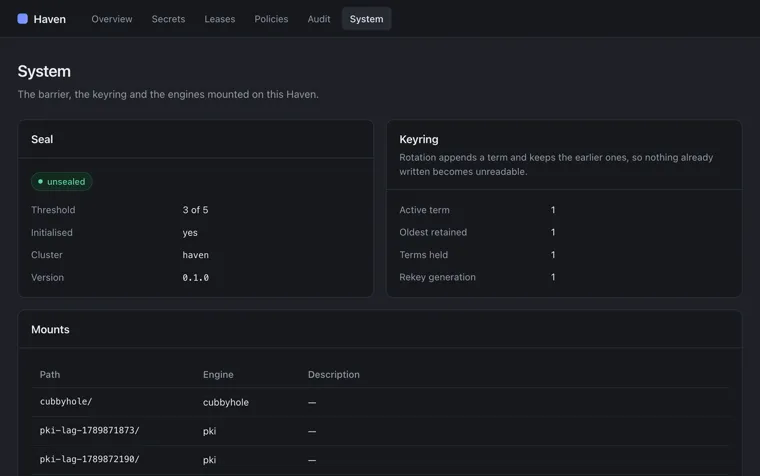
Seal, keyring and mounts Haven screenshot